September 4, 2026
When a Bad ROA Looks Like a Nation-State Attack
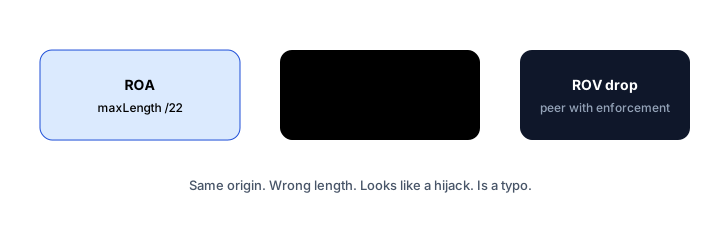
The timeline is always the same. A site dies in Europe and works in a café on LTE. Slack fills with the word “attack.” Someone pastes a threat-intel blog from 2018. Then a grown-up checks the ROA and finds a maxLength that no longer covers the /24 you announced at 14:00. You did this to yourself with a form on an RIR portal.
The split-brain that fools executives
RPKI Route Origin Validation is uneven. Some transits drop invalid. Some only depreference. Some ignore it. Users on LTE through a relaxed carrier still reach you. Users on a strict research network or a careful cloud region do not. That pattern feels targeted. It is adoption math.
A real hijack can look similar. The difference is the origin. A typo ROA usually keeps your ASN and breaks length. A hijack usually introduces a stranger ASN. Check both on the RPKI Validator and BGP Lookup before you wake the wrong team.
How a “security incident” becomes a ticket to the RIR
- Confirm the covering prefix and origin still match inventory.
- Validate the ROA. Invalid plus your own ASN is homework. Invalid plus a stranger is a hijack drill.
- Compare looking-glass views. If only enforcing regions are blind, stop writing press statements.
- Fix the ROA or withdraw the too-specific announce. Wait for caches. Do not “mitigate” by announcing an even longer prefix you also did not authorize.
AI dashboards will make this louder
New monitoring products summarize BGP in English. They are quick to say “possible hijack” because that sentence gets clicks. Teach yours the boring branch: invalid + expected ASN + recent ROA edit = operator error. Save “nation-state” for stranger origins, fresh more-specifics, and paths that never appear in your peering set.
Hygiene so this is boring next time
ROA maxLength should match what you actually announce. Two origins for multihoming need two ROAs. Schedule a validator check after every change window, not after Twitter. If a host announces on your behalf, they must be on the ROA or they will become an outage the first time a peer enables drop-invalid.
Validate the prefix you think is “under attack” on the RPKI Validator. Invalid and still your ASN is not theater. It is a form.
FAQ
Can a valid ROA still be a hijack?
Origin can be valid while the path is a leak. ROAs do not prove the whole AS path. They prove the origin is authorized for that length.
Should we turn off ROV after we self-own?
No. Fix the object. Turning off ROV to hide a typo trains you to do it again.